Critical PHP Security Vulnerabilities Discovered: Website Owners Urged to Update Immediately
Published: October 23, 2026 | Category: Cybersecurity
A major PHP security alert has raised concerns for website owners, developers, and web hosting providers worldwide. On October 21, 2026, the PHP development team released emergency security updates addressing two critical vulnerabilities that could allow attackers to execute malicious code on vulnerable servers without authentication.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, have prompted urgent warnings from cybersecurity agencies. Organizations are being advised to identify affected systems and install the appropriate security updates as quickly as possible. <Cite refs={["turn307326search1","turn307326search2"]}/>
What Happened?
The vulnerabilities affect PHP, a widely used programming language that powers websites, content management systems, and web applications.
According to security advisories, the flaws involve memory-handling errors that could potentially allow remote attackers to execute arbitrary code on affected servers.
This is particularly concerning because successful exploitation may occur without an attacker first obtaining a legitimate account.
Reports published on October 22 also described a surge in exploitation attempts following public disclosure, increasing the urgency for organizations to secure their systems. However, attempted exploitation does not necessarily mean a particular website has been compromised. <Cite refs={["turn307326search4","turn307326news7"]}/>
Which PHP Versions Are Affected?
The PHP development team released security fixes for several supported release branches.
PHP branch| Fixed version
PHP 8.5| 8.5.12
PHP 8.4| 8.4.27
PHP 8.3| 8.3.36
PHP 8.2| 8.2.35
Administrators should check the official PHP advisory for the complete affected-version details. PHP 8.1 and older branches may require vendor-specific fixes or migration to a supported version. <Cite refs={["turn307326search0","turn307326search5"]}/>
Who Is at Risk?
The issue is relevant to organizations operating PHP-based websites and applications, including:
- WordPress websites and other PHP-based content management systems
- E-commerce platforms and online stores
- Business websites and web applications
- Shared hosting and reseller hosting environments
- VPS, dedicated servers, and cloud hosting infrastructure
- Servers running PHP through PHP-FPM, Apache, CGI, LiteSpeed, or other supported configurations
The exact exposure depends on the PHP version, deployment configuration, and available vendor patches. Website owners should not assume they are protected simply because their application itself is up to date.
What Should Website Owners and Hosting Providers Do?
Security agencies recommend taking immediate action to identify vulnerable systems and apply the appropriate fixes. <Cite refs={["turn307326search1","turn307326search5"]}/>
1. Check your PHP version. Review your hosting control panel, server configuration, or command-line tools to identify the PHP versions used by websites and applications.
2. Install the security updates. Upgrade to the appropriate patched release or apply a verified vendor-provided fix.
3. Contact your hosting provider. If you use shared hosting or reseller hosting, ask whether the server's PHP runtime has been patched.
4. Review security logs. Look for suspicious requests, unexpected processes, unfamiliar files, unusual accounts, or unexpected outbound network connections.
5. Back up important data. Maintain protected backups and verify that your restoration process works.
6. Isolate systems if necessary. If a vulnerable internet-facing system cannot be patched promptly, consider restricting or temporarily disabling access until it can be secured.
Updating PHP is the priority. Security monitoring and backups are additional safeguards, not substitutes for installing the fix.
What Does This Mean for the Web Hosting Industry?
This incident highlights the importance of proactive security management across the hosting industry.
Hosting providers may operate hundreds or thousands of customer websites on shared infrastructure. Consequently, identifying vulnerable PHP installations and applying updates across supported environments can be an important operational task.
Website owners should also remember that PHP is only one part of website security. Outdated plugins, vulnerable themes, weak passwords, exposed administrative interfaces, and poor access controls can create additional risks.
Final Thoughts
The latest PHP security alert is a reminder that software maintenance is essential for protecting websites and online services.
Website owners, developers, and hosting providers should review their PHP environments, apply the appropriate security updates, and investigate suspicious activity where necessary.
For organizations that depend on PHP-based applications, acting promptly can reduce exposure to a serious and avoidable security risk.
Follow Ekuraa for the latest technology news, cybersecurity alerts, cloud computing updates, and web hosting guides.
Suggested tags: PHP, Cybersecurity, Security Vulnerability, Web Hosting, Server Security, Technology News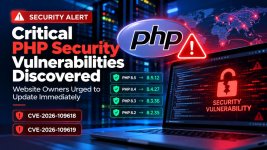
Published: October 23, 2026 | Category: Cybersecurity
A major PHP security alert has raised concerns for website owners, developers, and web hosting providers worldwide. On October 21, 2026, the PHP development team released emergency security updates addressing two critical vulnerabilities that could allow attackers to execute malicious code on vulnerable servers without authentication.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, have prompted urgent warnings from cybersecurity agencies. Organizations are being advised to identify affected systems and install the appropriate security updates as quickly as possible. <Cite refs={["turn307326search1","turn307326search2"]}/>
What Happened?
The vulnerabilities affect PHP, a widely used programming language that powers websites, content management systems, and web applications.
According to security advisories, the flaws involve memory-handling errors that could potentially allow remote attackers to execute arbitrary code on affected servers.
This is particularly concerning because successful exploitation may occur without an attacker first obtaining a legitimate account.
Reports published on October 22 also described a surge in exploitation attempts following public disclosure, increasing the urgency for organizations to secure their systems. However, attempted exploitation does not necessarily mean a particular website has been compromised. <Cite refs={["turn307326search4","turn307326news7"]}/>
Which PHP Versions Are Affected?
The PHP development team released security fixes for several supported release branches.
PHP branch| Fixed version
PHP 8.5| 8.5.12
PHP 8.4| 8.4.27
PHP 8.3| 8.3.36
PHP 8.2| 8.2.35
Administrators should check the official PHP advisory for the complete affected-version details. PHP 8.1 and older branches may require vendor-specific fixes or migration to a supported version. <Cite refs={["turn307326search0","turn307326search5"]}/>
Who Is at Risk?
The issue is relevant to organizations operating PHP-based websites and applications, including:
- WordPress websites and other PHP-based content management systems
- E-commerce platforms and online stores
- Business websites and web applications
- Shared hosting and reseller hosting environments
- VPS, dedicated servers, and cloud hosting infrastructure
- Servers running PHP through PHP-FPM, Apache, CGI, LiteSpeed, or other supported configurations
The exact exposure depends on the PHP version, deployment configuration, and available vendor patches. Website owners should not assume they are protected simply because their application itself is up to date.
What Should Website Owners and Hosting Providers Do?
Security agencies recommend taking immediate action to identify vulnerable systems and apply the appropriate fixes. <Cite refs={["turn307326search1","turn307326search5"]}/>
1. Check your PHP version. Review your hosting control panel, server configuration, or command-line tools to identify the PHP versions used by websites and applications.
2. Install the security updates. Upgrade to the appropriate patched release or apply a verified vendor-provided fix.
3. Contact your hosting provider. If you use shared hosting or reseller hosting, ask whether the server's PHP runtime has been patched.
4. Review security logs. Look for suspicious requests, unexpected processes, unfamiliar files, unusual accounts, or unexpected outbound network connections.
5. Back up important data. Maintain protected backups and verify that your restoration process works.
6. Isolate systems if necessary. If a vulnerable internet-facing system cannot be patched promptly, consider restricting or temporarily disabling access until it can be secured.
Updating PHP is the priority. Security monitoring and backups are additional safeguards, not substitutes for installing the fix.
What Does This Mean for the Web Hosting Industry?
This incident highlights the importance of proactive security management across the hosting industry.
Hosting providers may operate hundreds or thousands of customer websites on shared infrastructure. Consequently, identifying vulnerable PHP installations and applying updates across supported environments can be an important operational task.
Website owners should also remember that PHP is only one part of website security. Outdated plugins, vulnerable themes, weak passwords, exposed administrative interfaces, and poor access controls can create additional risks.
Final Thoughts
The latest PHP security alert is a reminder that software maintenance is essential for protecting websites and online services.
Website owners, developers, and hosting providers should review their PHP environments, apply the appropriate security updates, and investigate suspicious activity where necessary.
For organizations that depend on PHP-based applications, acting promptly can reduce exposure to a serious and avoidable security risk.
Follow Ekuraa for the latest technology news, cybersecurity alerts, cloud computing updates, and web hosting guides.
Suggested tags: PHP, Cybersecurity, Security Vulnerability, Web Hosting, Server Security, Technology News